Skip to content

Firebase Security Rules Audit + Fix PR · fixed price

Firebase Security Rules audit, with the fixes as a pull request

Apps built quickly on Firebase often ship rules that check whether someone is signed in, not whether the data is theirs. This audit tests your Firestore and Storage rules the way an attacker would, on the emulator, and hands back a fix that passes the tests.

Full refund if Simon can’t take it on once he sees your project, or if you cancel before work starts. Refund terms.

Check fit by email

$950 fixed price, 5 business days from repo access. Runs on the emulator only.

Work starts as soon as payment and the access arrive.

Price checked .

No call needed. Ask a question first by email at simon@app369.com or with the contact form; Simon replies by email, usually within one business day.

Short answer

The Firebase Security Rules Audit tests whether one signed-in user can read or change another customer's data in the Firestore and Storage rules of one Firebase project, then fixes what it finds. It costs $950 and takes 5 business days, with a report ranked by severity and a pull request. It fits apps built quickly on Firebase.

Firebase Security Rules Audit + Fix PR

Apps built quickly on Firebase often ship with rules that let one signed-in user read or edit another customer’s data. This audit tests whether yours does, and fixes what it finds.

$950
fixed price, 5 business days

Scope

  • Firestore and Storage rules, plus up to 15 Cloud Functions, in one Firebase project

You get

  • A written role and tenant access model
  • An emulator test suite that tries cross-user reads and writes, cross-tenant reads and writes, and role escalation
  • A report ranked by severity
  • A pull request with rule fixes that passes the suite
  • One revision round

Not included

  • Compliance certification
  • Infrastructure outside Firebase
  • App refactors

Delivery

5 business days.

Everything runs on the emulator or test data only, never your production records.

This is a technical review, not a compliance certificate.

Pay $950 & start

Full refund if Simon can’t take it on once he sees your project, or if you cancel before work starts. Refund terms.

After you pay

  1. You pay on Stripe and get the receipt by email.
  2. Simon emails you within one business day to confirm and send the access checklist. You can also send it straight away to simon@app369.com.
  3. Timeline: 5 business days.

What the work needs:

  • Access to the repository with your Firebase rules and Cloud Functions
  • Which Firebase project it covers, and the roles your app has (for example owner, member, client)

Delivery takes 5 business days from repo access. Production is never touched.

Full refund if Simon can’t take it on once he sees your project, or if you cancel before work starts. Refund terms.

Your code stays private: it is never shared or reused, and Simon deletes his copy at delivery. An NDA is fine; send yours with the access.

Not sure it fits? See who it fits, or email a question about this offer; Simon replies by email, usually within one business day.
This fits when

  • Your rules mostly check request.auth != null
  • You added teams, workspaces or roles after launch
  • A customer, investor or security questionnaire asks how tenant data is isolated
  • You can’t say for sure what a signed-in user could read with the Firebase SDK

Errors this fixes

Each page explains the error from the vendor’s own docs, with what to try first.

How it works

  1. Pay and share the repo

    Repo access to the Firebase project’s rules and functions is all that’s needed. No production access.

  2. Write the access model

    Who should read and write each collection and Storage path, by role and tenant, written down so you can check it.

  3. Attack it on the emulator

    A test suite tries cross-user reads and writes, cross-tenant reads and writes, and role escalation against your current rules.

  4. Report and fix PR

    Findings ranked by severity, and a pull request with rule fixes that passes the suite. The suite stays in your repo for future changes.

See what gets tested

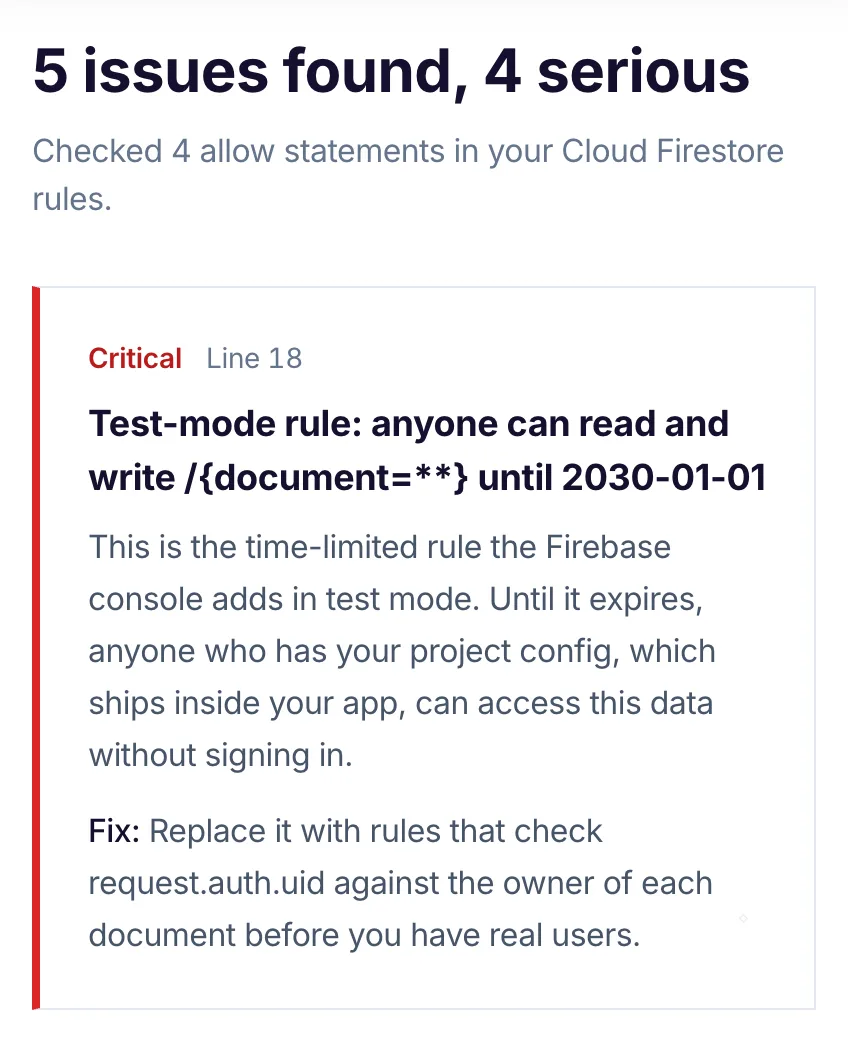
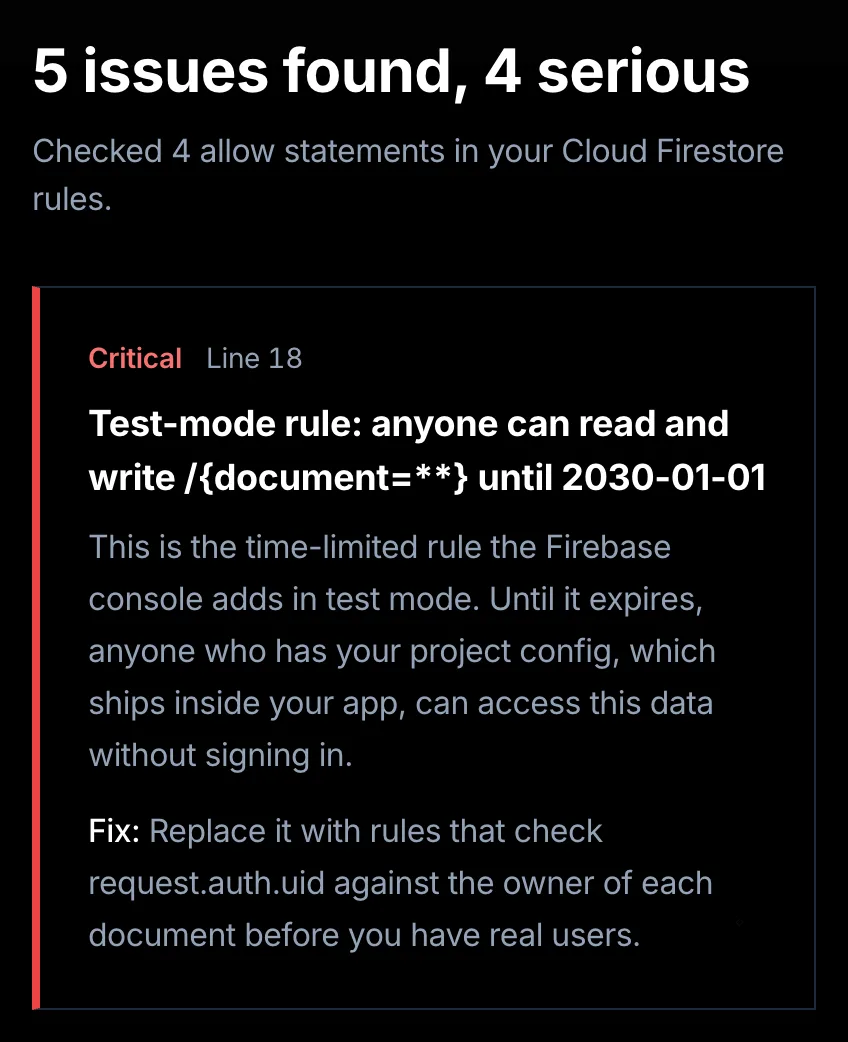
The free Firebase Security Rules checker reads your rules in your browser and flags the common mistakes. This is its real result on the example rules built into the tool. The audit goes further: it writes down who should access what, attacks your rules on the emulator, and fixes what fails.

Run the free checker on your rules

Firebase Security Rules checker result: 5 issues found, 4 serious. The first, critical on line 18, is a test-mode rule that lets anyone read and write every document until 2030-01-01.

Questions before you pay

Is this a compliance certificate?
No. It is a technical review of your rules with tests and fixes, not SOC 2, HIPAA or any other certification.
How many Cloud Functions are covered?
Firestore and Storage rules plus up to 15 Cloud Functions in one Firebase project. Larger projects get a written quote first, so email the repo link before you pay if you have more than 15.
Will you touch production?
No. Everything runs on the Firebase Emulator Suite or test data. You deploy the fixed rules yourself.
Is my code kept private?
Simon asks only for the access the work needs: the repository, plus read-only or test-mode access where the offer lists it. Production keys are never asked for. Your code is never shared or reused, and Simon deletes his local copy at delivery, when you can remove his access. An NDA is fine; send yours with the access.
Do I need a call before I pay?
No. The scope, price and delivery time are on this page, and everything happens in writing. If you want to talk live, calls cost $100 per 15 minutes, paid upfront.
Who owns what you deliver?
You do. The code, videos and files delivered under this offer belong to you once paid.

Fiverr reviews / 3 hand-picked of 127

What buyers said about Simon’s development work

Read 126 of the 127 reviews
  • “Working with Simon makes everything run so smoothly and better than I could ask for it. Amazingly communicative, extremely knowledgeable of coding and the backend processes. I strongly recommend.”
    A buyer in the United States, January 2026. App development on Fiverr
  • “Working with Simon has been an absolute pleasure. He’s not only incredibly skilled with his code, but he also brought so much care and attention to detail, especially when creating a custom section template for my Shopify site. He made the entire process smooth and collaborative, and consistently went above and beyond to make sure everything looked and functioned beautifully, very much the way I've envisioned. Highly recommend him for anyone looking for thoughtful, top-notch development support!”
    A buyer in China, April 2025. Custom order on Fiverr
  • “Very responsive, attentive to fixing bugs, and completed the project as needed! Thank you!”
    A buyer in the United States, July 2022. Shopify on Fiverr

Ready to start?

Simon, a senior software developer who builds and runs the SaaS Workspace369 (live on the App Store and the web), does the work himself. After you pay:

  1. You pay on Stripe and get the receipt by email.
  2. Simon emails you within one business day to confirm and send the access checklist. You can also send it straight away to simon@app369.com.
  3. Timeline: 5 business days.

Full refund if Simon can’t take it on once he sees your project, or if you cancel before work starts. Refund terms.

Looking for something else? See all fixed-price offers